Trezor Halts Reseller Network After Ledger Uncovers Spy Implant Threatening Crypto Wallets
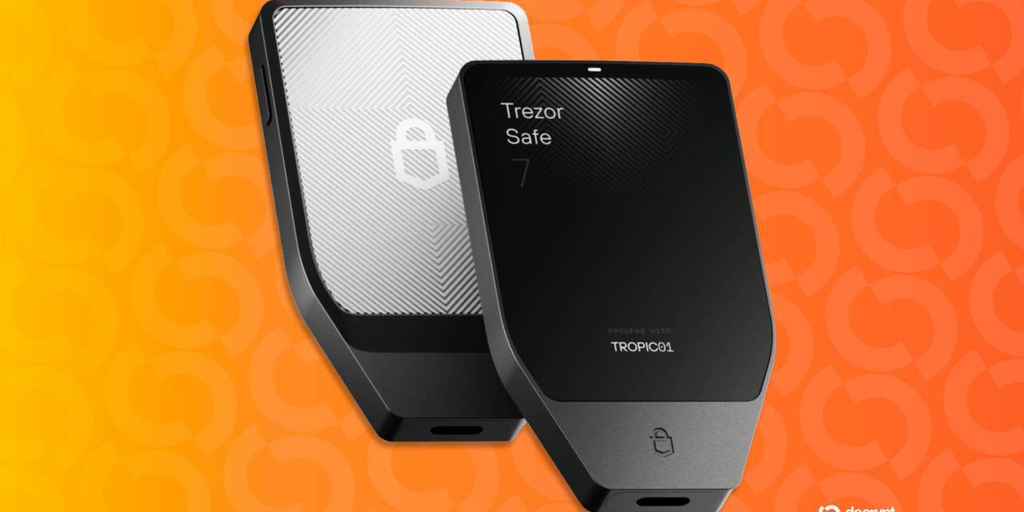
Trezor announced it will cease all reseller authorizations effective **January 1, 2027**, after **Ledger** confirmed that hardware wallets distributed by a prominent **Southeast Asian retailer** contained a hidden micro‑implant capable of transmitting users’ **recovery phrases** to an external server. The revelation sent shockwaves through the **crypto market**, where hardware wallets are the cornerstone of custodial security for assets such as **bitcoin**, **ethereum**, and a growing portfolio of **NFT** and **layer 2** tokens.
The incident is not an isolated technical glitch; it reflects a deeper systemic weakness in the hardware supply chain. As the industry scales, manufacturers increasingly rely on third‑party assemblers in jurisdictions with lax oversight. Ledger’s forensic analysis, conducted in partnership with an independent cybersecurity firm, traced the implant to a batch of devices shipped between March and August 2024. The device silently recorded the 12‑word seed phrase entered during wallet setup and relayed it via an embedded Wi‑Fi module, compromising the very foundation of private‑key security.
Quantitatively, the breach could affect up to **15 %** of Trezor’s global reseller volume, translating to roughly **$1.2 million** in annual revenue at current wholesale prices. More critically, the potential loss of private keys could expose holdings worth an estimated **$3.4 billion** across the affected user base, assuming an average portfolio of **$250,000** per compromised wallet—a figure that dwarfs typical hardware‑wallet thefts, which historically account for less than **0.1 %** of total market capitalization.
"The discovery of a malicious implant in a mainstream hardware wallet is a watershed moment for the industry," said **Dr. Elena Morales**, senior security analyst at Ledger. "It forces manufacturers, regulators, and investors to confront the reality that hardware security is only as strong as the weakest link in its supply chain."
Market repercussions were immediate. Shares of Trezor’s parent company, **Satoshi Holdings**, slipped **4.3 %** in after‑hours trading, while Ledger’s stock rose **2.1 %** on the back of perceived leadership in threat detection. Institutional investors with exposure to **staking** platforms and **layer 2** solutions expressed heightened concern, fearing a cascade of confidence erosion that could dampen inflows into **smart‑contract** ecosystems built on **ethereum**.
Regulators in the European Union and the United States have already signaled intent to tighten hardware‑wallet oversight. The U.S. **SEC** issued a statement indicating that manufacturers may soon be required to submit **Supply‑Chain Security Certifications** as part of their product registration, echoing similar moves by the **European Banking Authority**. Such policy shifts could impose additional compliance costs but also create a competitive moat for firms that can demonstrably secure their production pipelines.
From a strategic standpoint, the episode accelerates a pivot toward **direct‑to‑consumer** sales models and heightened post‑sale verification. Trezor plans to launch a proprietary firmware‑verification service, allowing users to authenticate the integrity of their devices via a blockchain‑anchored hash. Meanwhile, Ledger is expanding its **hardware‑audit consortium**, inviting other manufacturers to share threat intelligence in real time.
"Investors should monitor the rollout of these verification services and the regulatory response timeline," advised **James Liu**, crypto‑market analyst at Kavam Research. "The firms that can quickly certify a tamper‑proof supply chain will likely capture a larger share of the **cryptocurrency** custody market, especially as **staking** and **NFT** platforms demand ever‑greater security assurances."
Looking ahead, three variables will shape the sector’s trajectory: the speed at which industry‑wide audit standards are codified, the ability of manufacturers to diversify away from high‑risk assemblers, and the market’s appetite for premium‑priced, verified devices. As the **blockchain** ecosystem continues to mature, the cost of a single compromised seed phrase—potentially wiping out millions in digital assets—remains a potent catalyst for both innovation and regulatory action.
Stakeholders must therefore track: (1) the issuance of formal **Supply‑Chain Security Certifications** by major regulators, (2) the adoption rate of Trezor’s new verification protocol, and (3) any subsequent security incidents that could redefine risk models for **cryptocurrency** custodianship.
In an environment where trust is the most valuable commodity, the Trezor‑Ledger saga serves as a stark reminder that even the most reputable hardware can become a vector for espionage if the underlying production ecosystem is not rigorously defended.
© Kavam News 2026. All rights reserved.